
Tax Directorate General Denies Coretax Data Leak
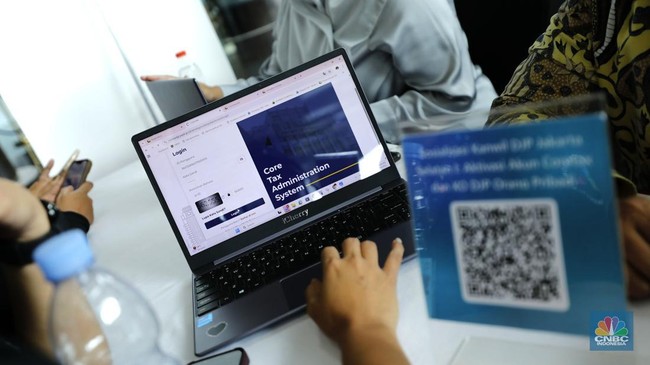
The Directorate General of Taxes (DJP) has denied the veracity of reports concerning the leakage of taxpayer data within the core tax administration system, known as Coretax.
“Regarding the information concerning the alleged data breach circulating on social media, the DJP has conducted internal examinations and validations, and the results allow us to state that this information is untrue,” stated the Director of Extension, Services, and Public Relations of the DJPS, Inge Diana Rismawanti, to CNBC Indonesia on Monday (21/09/2026).
Furthermore, Inge stated that this conclusion is based on the fact that the structure of the circulating data contains certain attributes or fields that are never stored or managed within the Directorate General of Taxes’ database.
“Data from the sample also shows the presence of users and passwords in plain text; clearly, this does not originate from the DJP Database system.”
The DJP ensures that the protection and confidentiality of taxpayer data remains a priority for the tax authority.
“The management of DJP information security refers to applicable information security standards and implements multi-layered security,” Inge emphasised.
The DJP has urged taxpayers to remain calm, maintain the confidentiality of their personal data, activate two-step authentication on the DJP Coretax system, and remain vigilant against links, messages, or requests for information claiming to be from the DJP.
The issue of the Coretax data leak was circulated on the X platform by @DailyDarkWeb. In a post on Saturday (19/09/2026), the account claimed that the database of the Indonesian tax authority had allegedly been breached, with passwords and authentication tokens claimed to have been stolen.
“A threat actor has uploaded what they claim to be a sample from a database associated with the Directorate General of Taxes (DJP) Indonesia, a unit under the Ministry of Finance,” the post stated on Monday (21/09/2026).
It was mentioned that the leaked data included NPWP (Taxpayer Identification Number), names and email addresses, phone numbers and physical addresses, passwords, user IDs, IP addresses, last login information, authentication tokens, ‘remember-me’ tokens, and account creation and update timestamps.
Nevertheless, the account stated that it had not independently determined the number of affected accounts, the source system, password format, token validity, or whether the material originated from a direct compromise of Indonesia’s tax infrastructure.