
Presidential Wiretapping Scandal Raises Concerns Over Pegasus Spyware
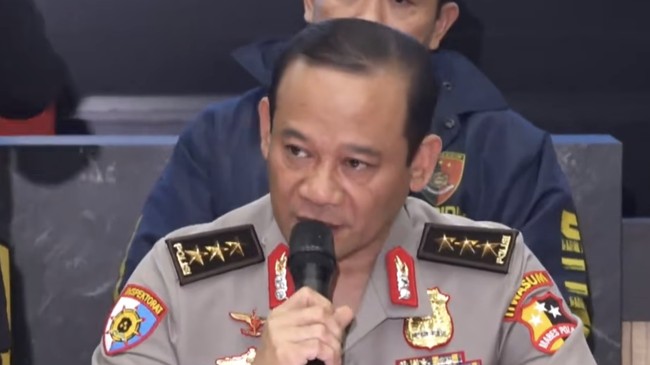
Jakarta, CNBC Indonesia — Indonesians have been alarmed by the naming of former National Police chief Listyo Sigit Prabowo as a suspect in an illegal wiretapping case involving, among others, President Prabowo Subianto. The case has brought renewed public attention to Pegasus, an Israeli-made surveillance tool described as one of the world’s most advanced, capable of infiltrating the phones of prominent figures around the globe.
The Indonesian National Police’s Criminal Investigation Department has named three people as suspects in an alleged criminal case involving illegal wiretapping, the deletion of electronic data and illegal access. The announcement was made by Criminal Investigation Department chief Commissioner General Asep Safrudin at a press conference at National Police headquarters in South Jakarta on Tuesday (3 November 2026).
He said the suspects were allegedly involved in procedurally unauthorised interception of the phone numbers of several people, including the Indonesian president, state officials, political figures, media organisations, mass-organisation figures, non-governmental organisations and businesspeople.
The case recalls media reports in 2023 about the entry of Pegasus spyware into Indonesia. Pegasus reportedly arrived in two devices belonging to Q Cyber Technologies Sarl via Soekarno-Hatta Airport in 2020, under code UKHI 1212635.
Pegasus is spyware developed by Israel-based NSO Group. The Economic Times has described it as the most powerful spyware ever created, capable of infiltrating both Android and iOS phones.
Spyware is software designed to breach a mobile phone’s security defences through a “back door”. An infected phone sends information about its owner’s activities to a third party.
Pegasus can exploit previously unknown bugs in operating systems. As a result, a phone may remain vulnerable even after security patches have been installed.
Pegasus was first reported in 2016 by The Citizen Lab, a Canadian cybersecurity organisation. The spyware had infiltrated the phone of human rights activist Ahmed Mansoor. In September 2018, the same organisation reported that Pegasus had infected devices in 25 countries.
The infections reportedly used spear-phishing techniques, sending text messages or emails containing malicious links. In 2019, Pegasus was reported to have infiltrated WhatsApp and to be capable of deleting missed-call records. The latest version can reportedly infiltrate a phone even if its target does not click a phishing link, in what is known as a zero-click attack.
NSO Group is on a US government blacklist over its involvement in activities deemed contrary to US national security interests or foreign policy.
Other advanced spyware in circulation includes Chrysaor and Phantom. These tools are all developed by private companies and are widely used.
Kaspersky has outlined several measures people can take to reduce the risk of surveillance by sophisticated spyware:
First, restart mobile devices every day. Rebooting helps “clean” the device, meaning an attacker would have to keep reinstalling Pegasus; this could increase the likelihood that a security solution would eventually detect the infection.
Keep mobile devices updated and install the latest patches as soon as they are released. Some exploit kits can target vulnerabilities that have already been patched, but users of older phones who delay updates remain at greater risk.
Never click links received in messages. This simple advice can be effective: some Pegasus customers rely more on one-click exploits than on zero-click attacks. Such links may arrive by SMS, other messaging services or email. If you receive an intriguing message with a link, open it on a desktop computer, preferably using the Tor Browser, or, better still, a secure non-persistent operating system such as Tails.
Use an alternative web browser for internet searches. Certain exploits do not work as well in alternative browsers such as Firefox Focus as they do in more conventional browsers such as Safari or Google Chrome.
Always use a VPN, as this makes it harder for attackers to target users based on their internet traffic. When choosing a VPN, consider a reputable service that has been operating for some time, accepts cryptocurrency payments and does not require registration information.
Install security software that can check whether a device has been jailbroken and issue an alert. Attackers using Pegasus may jailbreak a targeted device to maintain access; users with security software installed may receive a warning about such an attack.
If you use iOS, periodically trigger sysdiags and save them to an external backup. Forensic artefacts may help identify whether you have been targeted. Kaspersky experts also recommend that at-risk iOS users disable FaceTime and iMessage. Because these services are enabled by default, they have for years provided a means of delivering malicious zero-click attack chains.
Source: jawawa.id (https://jawawa.id/newsitem/presidential-wiretapping-scandal-raises-concerns-over-pegasus-spyware-1793753470)
Originally published by CNBC Indonesia (https://www.cnbcindonesia.com/tech/20261104061336-37-782083/geger-kasus-penyadapan-presiden-waspada-spyware-pegasus), translated from Indonesian