
KAI Strengthens Customer Data Security with ISO 27001 and Cyber Response Team
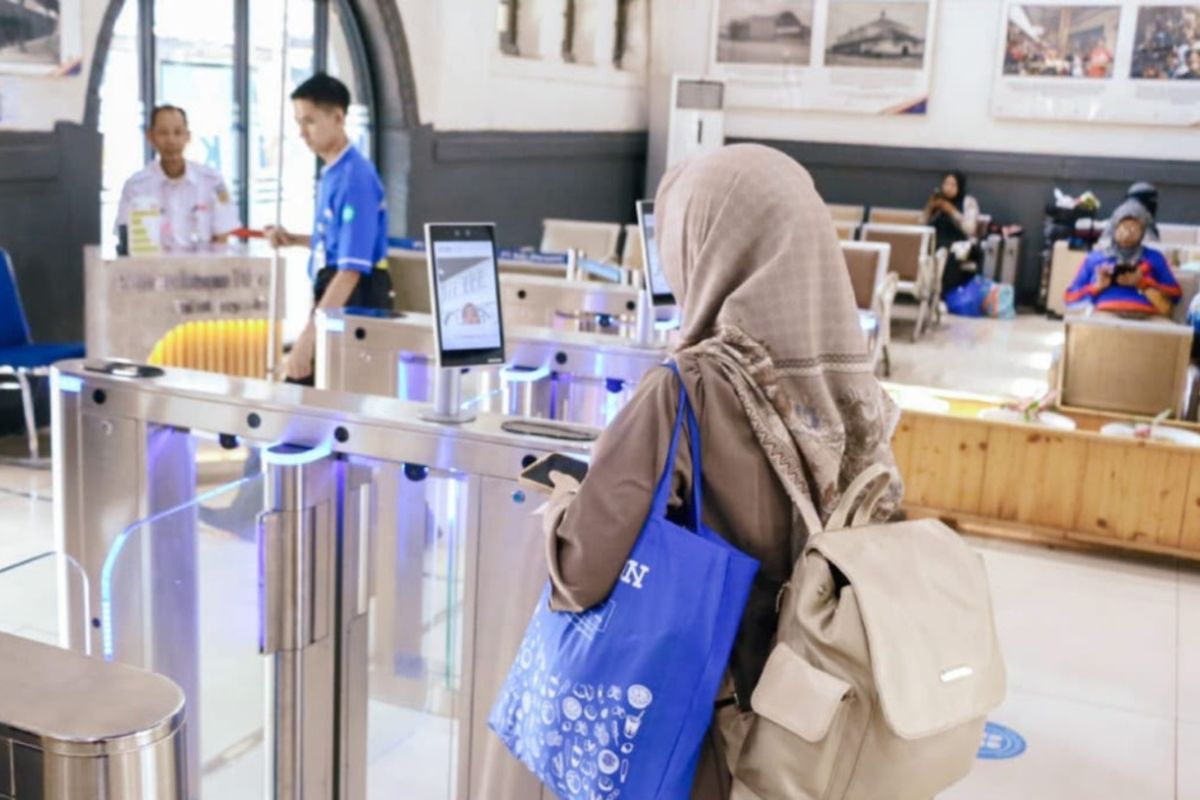
CSIRT, a Data Protection Officer, and regular security testing support the protection of information within KAI’s digital services.
Jakarta (ANTARA) - PT Kereta Api Indonesia (Persero) continues to strengthen the security and confidentiality of customer data as the use of digitally based travel services grows ever wider. These measures encompass data protection policies, system security, access control, cyber incident handling, and providing customers with clear information about how their data is used.
Vice President of Corporate Communication at KAI, Anne Purba, said that digitalisation has made the travel process easier, from searching schedules and buying tickets to payment, journey management, and boarding. This development must be accompanied by responsible data management.
“Customers entrust a certain amount of information to KAI when using digital services. We safeguard that trust through strengthened systems, governance, staff competence, and continuously evaluated data protection mechanisms,” said Anne.
In its 2025 Sustainability Report, KAI stated that developments in digital technology bring risks of cyber attacks, software vulnerabilities, and potential misuse of personal data. For this reason, the security and confidentiality of customer data is one of the main concerns in managing KAI’s digital services.
The customer data protection policy is also communicated through the Privacy Policy section of Access by KAI. This information helps customers understand the types of data managed, the purposes of use, retention periods, and how to request data deletion.
This step aligns with the spirit of the 81st Anniversary of the Independence of the Republic of Indonesia, “Indonesia Berdaulat, Adil, dan Makmur” (A Sovereign, Just, and Prosperous Indonesia). In economic development and digital services, sovereignty is also linked to the nation’s ability to manage technology and safeguard citizens’ information responsibly.
According to KAI’s internal data, throughout January–June 2026 some 5,555,034 long-distance train customers used the Face Recognition Boarding Gate.
The facility eases the boarding process because customers’ identities can be verified through facial data linked to their travel tickets. Registered customers no longer need to show a boarding pass, e-boarding pass, or ID card to staff when passing through the Face Recognition Boarding Gate.
The use of Face Recognition is optional. Customers choosing the service must give their consent during registration via Access by KAI, Check-in Counter machines at stations, or Customer Service staff.
“Customer consent is an essential part of the Face Recognition service. Customers can still use other available boarding mechanisms if they do not register their facial data,” said Anne.
The data used for Face Recognition includes name, National Identity Number (NIK), and facial photograph. The 2025 Sustainability Report explains that this data is stored within KAI’s system infrastructure and used exclusively for Face Recognition Boarding Gate operations.
Face Recognition registration data is stored for one year and automatically deleted once the retention period ends. Customers may also request earlier deletion of their data through Access by KAI or by submitting a request to Customer Service staff at stations.
The expansion of digital services is also evident in the use of Access by KAI. As of 30 June 2026, the application had 30,449,049 registered users, with 9,058,935 active users and cumulative downloads reaching 41,011,320.
During the first semester of 2026, Access by KAI served 17,009,374 ticket transactions for Main and Local trains. This figure equates to 76.34 per cent of all transactions through the sales channels for these two services.
In terms of customer volume, 24,544,468 Main and Local train customers obtained tickets through Access by KAI between January and June 2026. That equates to 73.68 per cent of the customer volume across all sales channels for the two services.
According to Anne, the high usage of the application shows that digital services have become an important part of customers’ journeys. Access by KAI is currently used to obtain schedule information, buy and cancel tickets, change travel schedules, access e-boarding passes, register for Face Recognition, and use various supporting services within the KAI Group ecosystem.
“The wider the use of digital services, the greater KAI’s responsibility in safeguarding systems and customer data. Service convenience must go hand in hand with security, transparency, and respect for customers’ rights,” Anne explained.
KAI implements an Information Security Management System certified to the international ISO 27001 standard. This standard guides the management of information security risks, regulates access to data, and maintains the confidentiality, integrity, and availability of information.
Governance is also strengthened through the formation of a Computer Security Incident Response Team, or CSIRT. This team is tasked with handling, coordinating, and responding to any discovered cyber security incidents.
KAI has also appointed a Data Protection Officer (DPO), an official responsible for overseeing the implementation of company policy and compliance in data protection. According to the 2025 Sustainability Report, KAI’s information technology governance maturity level stands at approximately level 3.8.
Beyond organisational strengthening, KAI conducts regular vulnerability assessments and security testing of its systems. These checks aim to identify potential gaps in applications and digital infrastructure so they can be addressed before disrupting services or posing risks to customer information.
Customer data management is carried out in accordance with Law Number 27 of 2022 on Personal Data Protection as well as internal company policies. KAI also continues to educate its workforce on information security, access management, and responsibilities in processing data.
“KAI will continue to strengthen technology, governance, and incident response readiness as digital services develop. For KAI, safeguarding customers’ journeys also means safeguarding the information entrusted to the company,” Anne concluded.
Source: jawawa.id (https://jawawa.id/newsitem/kai-strengthens-customer-data-security-with-iso-27001-and-cyber-response-team-1785830088)
Originally published by Antara (Indonesian) (https://www.antaranews.com/berita/5679063/kai-perkuat-keamanan-data-pelanggan-terapkan-iso-27001-dan-bentuk-tim-respons-siber), translated from Indonesian