
GP Ansor Calls for Public Participation in Cybersecurity Bill Deliberations
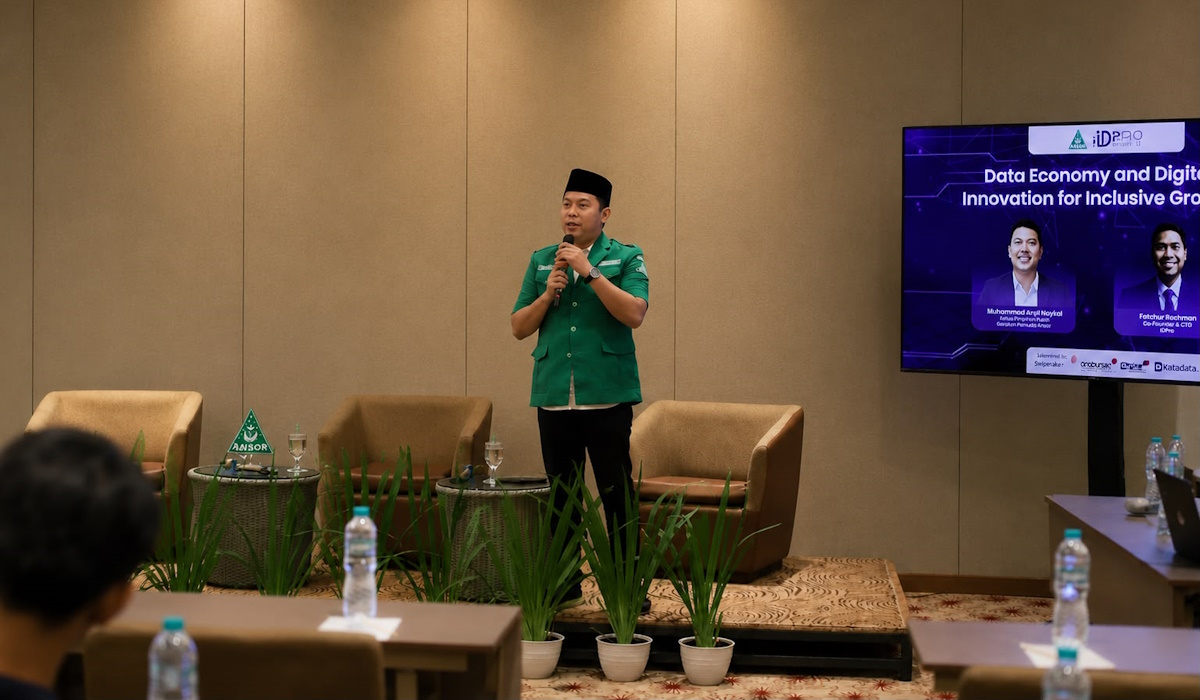
The Cyber Body of the Central Leadership of GP Ansor (PP GP Ansor) believes that the discussion process for the Cyber Security and Resilience Bill does not prioritise the principles of transparency and public participation. As a strategic regulation that will serve as the foundation for national cyber security governance, the discussion of the Bill should be conducted openly to obtain input from all stakeholders.
The Head of the Cyber Body of PP GP and Ansor, Ahmad Luthfi, stated that cyber security is no longer an issue solely concerning national defence, but has become a matter that directly affects the lives of the public. Therefore, regulations governing the national cyberspace must be drafted accountably and involve the public.
“The Cyber Security and Resilience Bill will become the legal foundation for Indonesia’s digital ecosystem in the long term. Regulations that have a wide impact on the digital rights of the community should not be discussed behind closed doors. Transparency is a primary requirement to produce high-quality, legitimate regulation capable of addressing national cyber security challenges,” said Ahmad Luthfi.
In his view, the lack of openness in discussions could potentially reduce the substance quality of the Bill because it fails to provide adequate space for academics, cyber security practitioners, digital industry players, civil society organisations, technology communities, and professional associations to provide meaningful input.
The Cyber Body of PP GP Ansor assesses that Indonesia has entered a new phase of cyber threats. In recent years, the public has faced various cases of personal data breaches, ransomware attacks on public services and the financial sector, digital fraud, phishing, identity theft, account takeovers, and the misuse of artificial intelligence through deepfakes and voice cloning.
These conditions indicate that the orientation of regulation should not only focus on state security but must also place human security as a top priority.
In addition to transparency, the Cyber Body of PP GP Ansor also encourages the drafting of the Bill to adopt best practices from various countries. Singapore has built a system for protecting critical information infrastructure accompanied by mandatory incident reporting. The European Union, through NIS2, has strengthened cyber security governance, digital supply chain security, and the accountability of organisational leaders. Australia has strengthened national cyber resilience through mandatory reporting and the protection of essential infrastructure, while the United States has developed a model of close collaboration between the government and the private sector in facing cyber threats.
“Indonesia must not only pursue the existence of a law, but also ensure that the law is capable of protecting the community, strengthening national resilience, and being adaptive to the development of global cyber threats. Good regulation is born from an open, participatory process based on public interest,” Ahmad Luthfi asserted.
The Cyber Body of PP GP Ansor is urging the House of Representatives (DPR RI) and the government to open public access to the draft of the Cyber Security and Resilience Bill, organise meaningful public consultations involving academics, the cyber security community, industry players, civil society organisations, and professional associations, and ensure that the ratified Bill truly becomes an instrument for public protection as well as a foundation for national cyber resilience in the digital era.