
Companies Urged to Strengthen GRC to Face Digital Risks
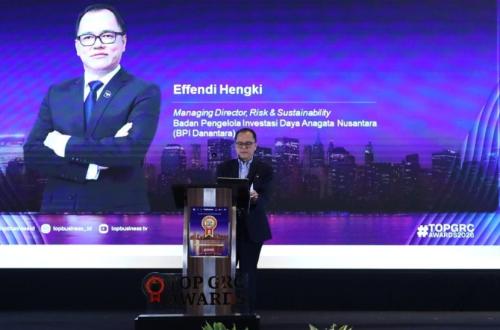
Companies in Indonesia are being urged to transform their approach to Governance, Risk, and Compliance (GRC) from periodic inspections towards continuous assurance. This approach is considered more suitable for the rapidly changing digital risks that can manifest in a very short timeframe.
Effendi Hengki, Managing Director of Risk & Sustainability at BPI Danantara, stated that organisations can no longer rely solely on historical sample-based inspections or snapshots to oversee risks.
“Risks such as data breaches, financial fraud, system configuration changes, or access issues can develop within minutes, necessitating a continuous oversight mechanism,” Effendi said during his keynote speech at the peak of the TOP GRC Awards 2026 in Jakarta on Wednesday (9/9/2026), according to a press release received on Saturday (12/9/2026).
According to Effendi, continuous assurance utilises data more broadly and in real-time, alongside automated validation and system integration. With this approach, oversight is not merely conducted ahead of audits but is integrated into daily operational activities.
Effendi noted that GRC needs to be positioned as part of strategic decision-making, rather than just a compliance function. Effective GRC management can help organisations measure risk, control potential losses, capture opportunities, and improve the quality of business operations.
The implementation of continuous assurance can be achieved through two mechanisms: Continuous Monitoring (CM) and Continuous Auditing (CA). Continuous Monitoring operates within the management and operational spheres to proactively detect deviations and changes in controls.
Meanwhile, Continuous Auditing provides ongoing independent testing of the effectiveness of the monitoring system. This function may involve internal audits, audit committees, and external auditors, depending on the organisation’s needs.
Effendi mentioned three key aspects to consider when building such a system: People & Culture, Process & Control, and Technology. Regarding people and culture, organisations need to enhance the understanding that compliance is an integral part of operational activities while strengthening data-driven audit capabilities.
In terms of process and control, organisations should possess a common control matrix and clear boundaries between processes that can be automated and those that still require human intervention. From a technological perspective, an API-first architecture and a ‘single source of truth’ can be utilised to support automated evidence retrieval and the provision of compliance information through integrated dashboards.
The application of continuous assurance can also be implemented through automated workflows, allowing for faster responses to changing risks. Through this approach, GRC can be used to strengthen organisational resilience and the quality of decision-making.
The peak of the TOP GRC Awards 2026, held in Jakarta, carried the theme “Sustainability by Design: A Journey Through Intelligent GRC”. A total of 108 companies received the TOP GRC Awards 2026. Now in its eighth year, the event also includes assessments, benchmarking, jury feedback, and the identification of areas where companies need further strengthening.
The Chairperson of the TOP GRC Awards 2026 stated that the awards do not only evaluate company achievements but also serve as a learning process. “The award is a form of appreciation for achievements. However, the assessment and judging process must provide added value in the form of insights and improvement agendas,” they remarked.
Furthermore, the concept of ‘Intelligent GRC’ was a key discussion point this year. This concept emphasises the use of data, technology, analytics, and Artificial Intelligence to enhance information quality, accelerate risk detection, and support decision-making.
Source: jawawa.id (https://jawawa.id/newsitem/companies-urged-to-strengthen-grc-to-face-digital-risks-1789228504)
Originally published by Republika (https://esgnow.republika.co.id/berita/tl9bch416/perusahaan-didorong-perkuat-grc-hadapi-risiko-digital), translated from Indonesian